The WAN Challenge – or how do I discover Remote Computers efficiently?
Introduction
Discovering Windows computers at remote sites can be much slower than scanning devices on a local network. WMI and Remote Registry are commonly used to collect inventory data, but over a low-bandwidth WAN connection even a simple registry request can take a long time. When many registry entries must be read to identify installed software, a scan of one computer may take far longer than is practical.
This article explains how JDisc Discovery uses its remote login capability to collect Windows inventory data efficiently when native remote access is slow or blocked.
Why WAN discovery can become slow
On a 100 Mbit/s or 1 Gbit/s Ethernet LAN, accessing WMI and registry information is usually not a problem. At remote locations connected by limited-bandwidth links, however, the round trips required by remote WMI and registry access can add up quickly.
Agent-based discovery products address this by installing a permanent agent locally. This can provide broad local access, but deployment and upgrades require additional work. Some devices, including routers, switches, and printers, do not support proprietary agents at all.
JDisc Discovery is a agentless discovery by default. For Windows computers, its remote login option can temporarily deploy a discovery agent while the target is scanned. After the scan, the agent removes itself and its temporary files.
How remote login works
When remote login is enabled for a Windows target, JDisc Discovery:
- Attempts to obtain administrative access through SMB.
- Deploys and starts the temporary discovery agent when access succeeds.
- Uses the agent to run native commands locally and to transfer collection binaries or results securely between the discovery station and target.
- Removes the agent and temporary files when the scan is complete.
The temporary agent is deployed automatically and requires no manual interaction on the target computer. This approach combines an agentless default model with local execution where it is useful for the current scan. For broader context on the product, see JDisc Discovery’s network inventory capabilities.
Enable remote login for Windows
Open the discovery settings dialog and select the Protocols tab. In the upper area, change the Windows selection to Windows Remote Login.
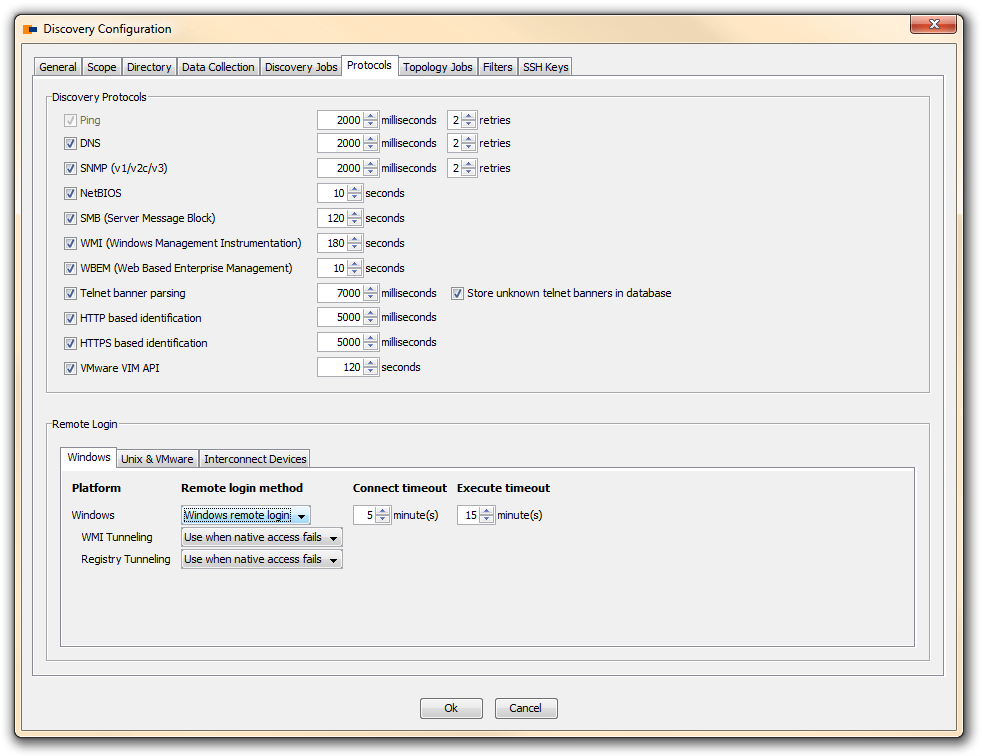
Enable remote login for Windows.
When remote login is useful
Remote login can help in several situations:
- Firewall restrictions: Native WMI uses several TCP/IP ports. If firewall rules block this traffic, remote WMI connections can fail with errors such as “The RPC server is unavailable.” JDisc Discovery’s remote login capability uses port 445 and can tunnel WMI and Remote Registry access through the temporary agent.
- Remote Registry is unavailable: Native registry access depends on the Remote Registry service. Remote login can read registry entries locally on the target while the temporary agent is running.
- Local Windows firewalls: Local firewall rules can block WMI traffic. The remote login tunnel can carry WMI requests over port 445.
- Slow WAN links: Running the relevant requests locally on the target avoids many expensive remote round trips. The original field tests described improvements of up to eight to ten times in suitable WAN scenarios; actual results depend on the network and target configuration.
Choose the appropriate tunneling setting
JDisc Discovery provides settings for WMI and registry tunneling:
- Use when native access fails is the default choice when you want tunneling only if native protocols fail, for example because of firewall restrictions.
- Use always uses the remote login tunnel for WMI or registry access regardless of native protocol status.
- Disabled prevents the use of tunnels for WMI or Remote Registry access.
This lets you adapt the collection method to the conditions at each site instead of treating all Windows computers the same way.
A practical approach to remote-site inventory
For remote Windows systems, start with native access where it works well and use remote login when WAN latency, firewall policies, or the Remote Registry service make native collection unreliable or inefficient. This gives you a way to keep discovery practical without introducing a permanently installed agent.
You can download a JDisc Discovery trial to evaluate the approach in your own network, or book a demo to discuss your requirements.
Frequently Asked Questions
These answers cover common questions about discovering remote Windows computers with JDisc Discovery across WAN links. They clarify how temporary remote login differs from a permanently installed agent and when the option can be useful.
JDisc Discovery is agentless by default. Remote login temporarily deploys a discovery agent during the scan of a Windows target and removes it and its temporary files when the scan finishes.
The remote login capability described here uses port 445 for SMB access and can tunnel WMI and Remote Registry access through the temporary agent.
It can help when native WMI traffic is blocked and SMB access over port 445 is available. The temporary agent can run relevant work locally and tunnel the access through the remote login connection.
The described remote login approach can read registry entries locally on the target while its temporary agent is running, including when the Remote Registry service is not running.
Select it when you want JDisc Discovery to use tunneling only after native WMI or registry access fails, such as in a firewall-restricted environment.
No. The remote login option in this article applies to Windows computers. Devices such as routers, switches, and printers generally cannot run proprietary discovery agents.
About The Author